LM Technologies Ltd
Vulnerability Disclosure Policy & PSIRT Guidelines
LM Technologies Ltd is committed to maintaining the security and integrity of our wireless communication products, embedded modules, firmware, and software tools. We value the contributions of security researchers and the broader cybersecurity community in helping us identify and remediate vulnerabilities responsibly.
This policy establishes the framework for discovering, reporting, and handling security vulnerabilities, while defining the responsibilities of the LM Technologies Product Security Incident Response Team (PSIRT).

1. Role of the Product Security Incident Response Team (PSIRT)
The LM Technologies PSIRT serves as the central focal point for receiving, investigating, coordinating, and disclosing security vulnerabilities across all LM Technologies product lines (including Bluetooth/Wi-Fi modules, adapter products, embedded firmware, and software development kits).
Key Responsibilities of the PSIRT:
- Single Point of Contact: Receiving security vulnerability disclosures from researchers, customers, and industry partners.
- Triage & Assessment: Evaluating reports using the Common Vulnerability Scoring System (CVSS v3.1/v4.0) to determine severity and scope.
- Remediation Coordination: Working directly with internal hardware, software, and firmware engineering teams to develop and test security updates or mitigations.
- Public Advisories: Publishing formal Product Security Advisories (PSAs) and coordinating CVE identifier assignments where applicable.
2. Scope
In-Scope
- Hardware: Physical hardware modules and adapters developed and sold by LM Technologies Ltd (e.g., LM811, LM842, LM068, etc.).
- Firmware: Official stack software, bootloaders, and firmware releases maintained by LM Technologies.
- Software: Configuration tools, host drivers, and SDKs provided for platform integration.
Out-of-Scope
- Third-party libraries, chipsets, or platforms not developed or directly maintained by LM Technologies (these should be reported to the respective upstream vendor).
- Volumetric Distributed Denial of Service (DDoS) attacks against web infrastructure.
- Social engineering, phishing, or physical physical security testing directed at LM Technologies employees or facilities.
- Vulnerabilities requiring destructive physical lab extraction techniques beyond standard interface/bus analysis.
3. How to Report a Vulnerability
If you believe you have identified a vulnerability in an LM Technologies product, please submit a detailed report to the PSIRT.
Submission Channel
- PSIRT Email:
partner.services@lm-technologies.com - Encrypted Communication: For sensitive disclosures or reports containing Proof of Concept (PoC) code, please encrypt your submission using the LM Technologies PSIRT PGP public key.
Required Information
To allow the PSIRT to triage and validate your submission quickly, include the following details:
| Information Field | Description |
| Product & Hardware Model | Exact product name, part number, and hardware revision. |
| Firmware/Software Version | Precise build version, firmware revision, or driver version tested. |
| Vulnerability Category | Classification (e.g., Buffer Overflow, Insecure Pairing, Logic Flaw, Privilege Escalation). |
| Reproduction Steps | Step-by-step instructions, trace logs, or PoC code necessary to reproduce the issue. |
| Impact Assessment | Potential consequences of exploitation (e.g., Remote Code Execution, Information Disclosure, DoS). |
4. PSIRT Handling Process & Response Timelines
LM Technologies PSIRT follows a structured Coordinated Vulnerability Disclosure (CVD) workflow:
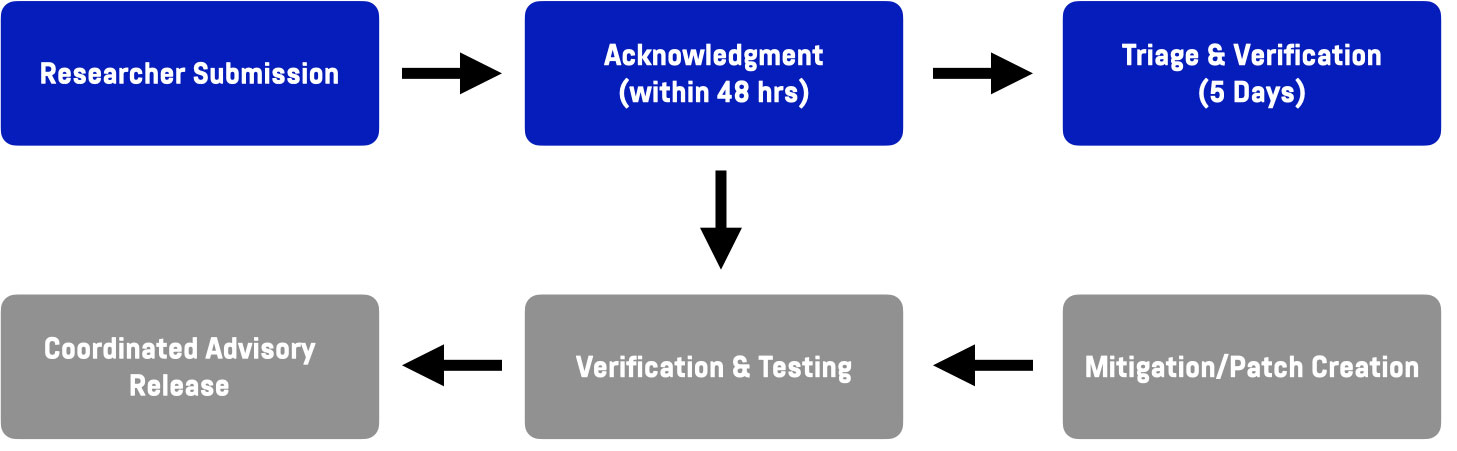
- Receipt Acknowledgment: The PSIRT will acknowledge receipt of your report within 48 business hours.
- Investigation & Triage: Within 5 business days, the PSIRT will confirm or deny the vulnerability, determine its severity, and assign an internal tracking ID.
- Remediation Phase: Engineering teams will develop, build, and validate a firmware/software update or engineering workaround.
- Coordinated Disclosure: LM Technologies targets patch deployment and public advisory release within 60 to 90 calendar days of report validation, working with the researcher to coordinate disclosure timelines.
5. Safe Harbor Commitment
LM Technologies PSIRT follows a structured Coordinated Vulnerability Disclosure (CVD) workflow:
LM Technologies Ltd considers security research conducted in accordance with this policy to be authorized. We commit to the following:
- No Legal Action: We will not pursue legal action against researchers who act in good faith, comply with applicable laws, and follow these disclosure guidelines.
- Privacy Protection: Researchers must avoid accessing, altering, or destroying customer data.
- Coordinated Timing: Researchers must refrain from public disclosure until LM Technologies has released an update or alternative mitigation, unless mutually agreed otherwise.